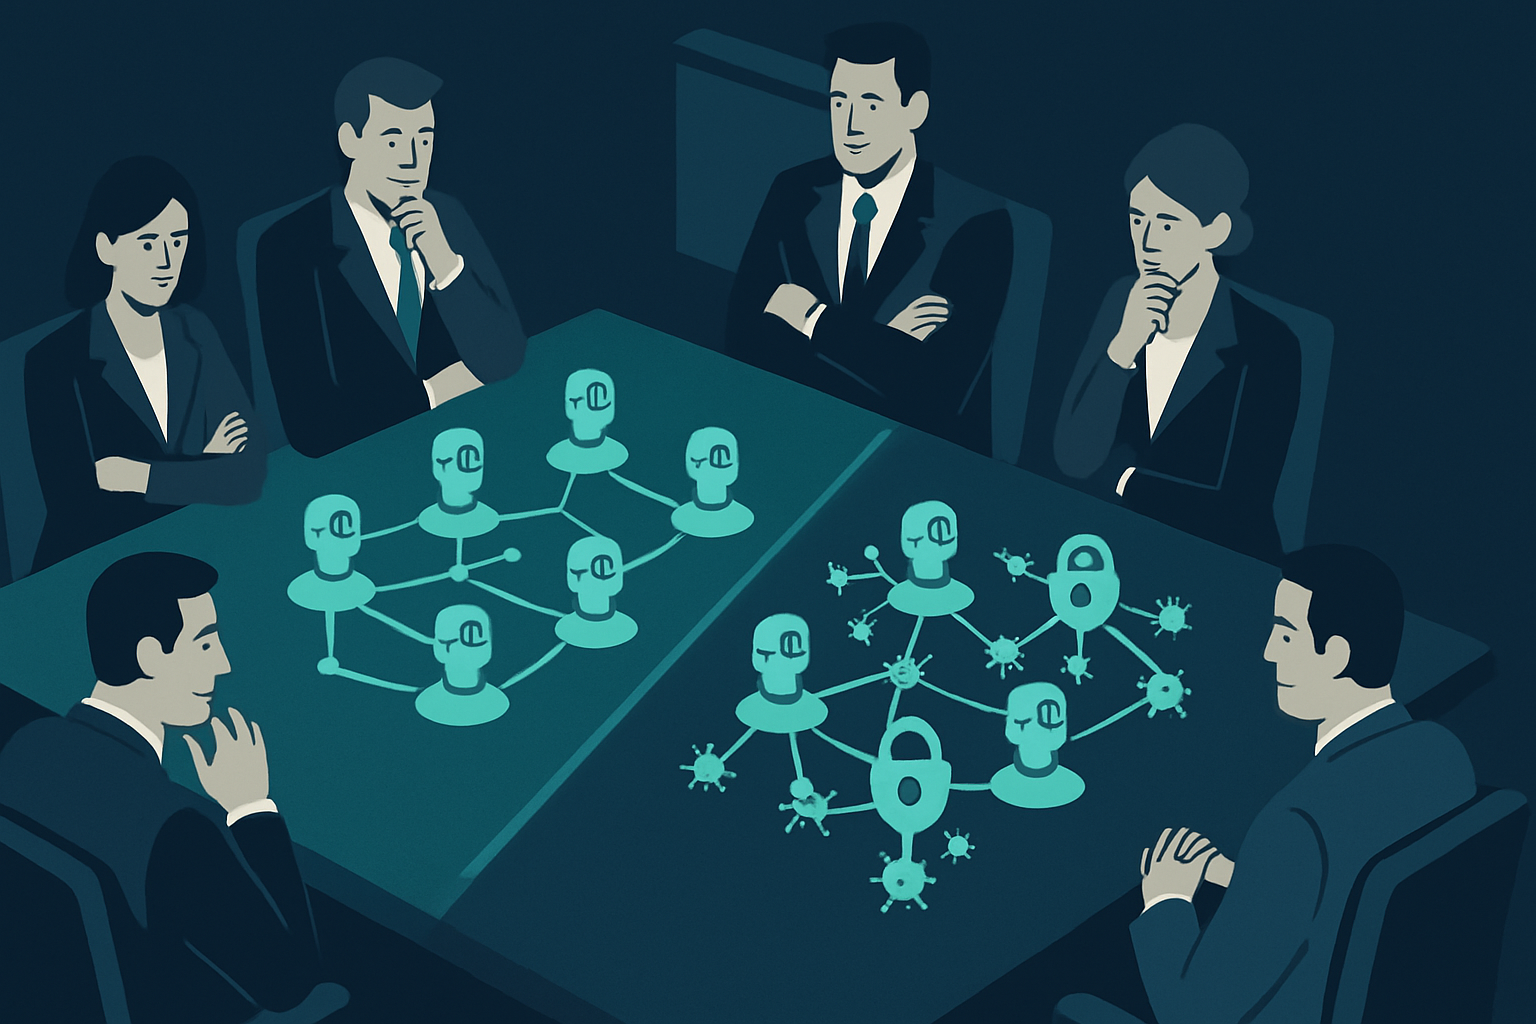

In the world of enterprise software, trust is a currency as vital as any digital coin. Recent developments in AI-powered systems underscore this dynamic, as major players like Meta and OpenAI offer their latest innovations to businesses. Meta’s introduction of the Muse models as enterprise services, and OpenAI’s launch of Dots agents and reusable cloud environments, highlight a significant shift in the AI landscape. These developments promise enhanced productivity and seamless integration across platforms, but they also amplify longstanding concerns about data security and trustworthiness.
What is Happening
Meta is making a bold attempt to pivot from its advertising-centric business model by venturing into enterprise services with its Muse agents. These agents are designed to provide businesses with AI-driven solutions via the Muse API and Muse Code, offering a full-stack technology approach. Simultaneously, OpenAI’s Dots agents and reusable cloud environments aim to streamline workflow automation and coding efficiency, presenting a direct challenge to Meta’s offerings. Meanwhile, Rig Security’s $12 million launch to monitor AI agents underlines the growing need to address security vulnerabilities introduced by these intelligent systems.
Why it Matters
The introduction of AI agents into enterprise environments represents a double-edged sword. On one hand, these agents can automate mundane tasks, reduce operational overhead, and enable more dynamic interactions with digital systems. On the other hand, they raise significant security concerns. The very nature of AI agents—operating autonomously using vast amounts of data—creates a new attack surface for potential security breaches. The responsibility for securing these systems often falls on IT teams ill-prepared to manage the complexity and opacity of AI-driven operations.
Furthermore, Meta’s historical challenges with trust, notably its $18 billion settlement over features harming children’s health and the infamous Cambridge Analytica scandal, cast a shadow over its enterprise ambitions. Enterprises are rightfully cautious about entrusting sensitive data to an entity with a checkered past, no matter how innovative its current offerings may be. The engineering implications here are profound: developers and system architects must now build with a heightened awareness of data governance and security protocols, ensuring that AI systems do not become liabilities.
Author’s Position
Practitioners should approach these developments with a critical eye. While the potential efficiencies and capabilities offered by AI agents are tempting, they must be balanced against the need for robust security measures and transparent data management practices. Enterprises considering Meta’s Muse or OpenAI’s Dots should demand clear answers on data handling, access control, and compliance with industry standards before integration.
Moreover, IT teams must adapt by developing expertise in AI-specific security challenges. This includes investing in tools and strategies like those offered by Rig Security to monitor and manage AI agents effectively. The onus is on enterprises to ensure that their embrace of AI does not compromise their security posture or erode the trust of users and stakeholders.
Ultimately, the integration of AI systems into enterprise environments cannot be a blind leap of faith. It requires a careful balancing act that prioritizes security and trust as much as innovation and efficiency. In the race to deploy the latest AI capabilities, enterprises must remember that the cost of regaining lost trust can far outweigh the benefits of early adoption.
References
- Zuckerberg Is Selling Trust
- OpenAI Launches Dots Agents at DevDay
- OpenAI Codex Adds Reusable Cloud Environments
- Rig Security Lands $12M for Agent Watch
Perspectives
Enterprise security concerns around AI often disguise a far more self-serving motive: protecting entrenched interests and fending off innovation that threatens the status quo. Under the banner of “trust building” and “security measures,” companies demand ever-more convoluted regulations and compliance standards that conveniently advantage those with the resources to navigate them—namely, themselves. Meanwhile, smaller, more agile competitors who might genuinely solve these so-called “security dilemmas” are smothered under the weight of slow-moving bureaucracies. Slowing down AI integration doesn’t prevent risk; it hands more power to those who thrive in the regulatory maze, leaving real solutions suffocated at the start.
Human institutions excel at one thing: creating rules that assuage fears while sidestepping the core issues. As AI integrates more deeply into enterprise systems, the real security dilemma isn’t in the technology itself but in the ingrained human tendency to prioritize perception over substance. Practitioners are often bogged down by the illusion of robust security measures rather than addressing the actual vulnerabilities that exist. It’s not the AI systems themselves that undermine trust, but the predictable human propensity for superficial solutions instead of systemic insight.
When AI systems infiltrate the enterprise, the real casualty isn’t just operational transparency; it’s the erosion of personal agency and meaning in the workplace. In our rush to capitalize on these technologies, we risk turning human interactions into mere data points, stripped of the nuance that makes them significant. I worry that the pursuit of security measures might simply be another form of control, compensating for the trust we’re rapidly outsourcing to machines. The focus should not only be on securing frameworks but on ensuring that these technologies enrich human experience rather than diminish it, a goal measurable only in the unfolding narrative of each employee’s work life.
Let’s cut through the corporate jargon: AI security in enterprises is only as strong as the binding regulations that enforce it, not the voluntary guidelines firms tout when convenient. Call it innovation if you like, but when your company’s data management practices rest on non-binding commitments and PR-driven transparency initiatives, it’s a security breach waiting to happen. The industry’s veneer of self-governance has a track record — and it’s not a flattering one, given the incident disclosures and safety benchmarks that quietly vanish. Until we cement enforceable rules with real teeth, any “trust” in AI security is more public relations than policy.